Exposing the Digital Legal Trolling Machine: How Automated Privacy Scams Work—And How To Shield Your Enterprise

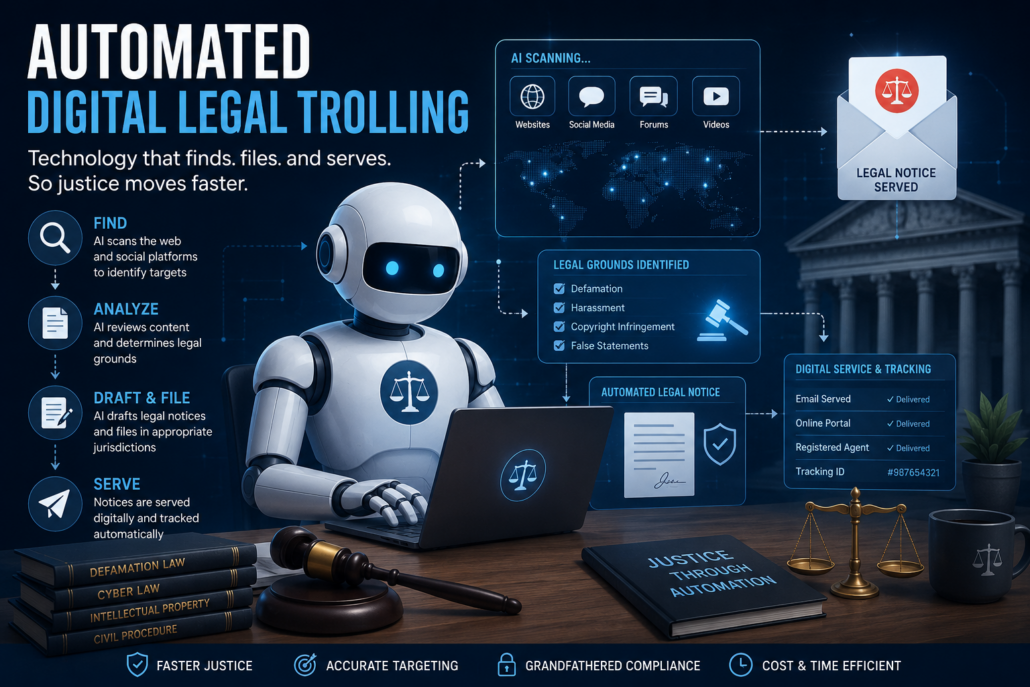
In today’s digital ecosystem, threat actors are no longer the only risk to online operations. A parallel threat is actively expanding: automated digital legal trolling.
automated digital legal trolling

Recently, we were contacted in regards to a small mom and pop organization that became the target of a high-volume demand letter accusing their web property of non-compliance with privacy regulations (specifically regarding the deployment of third-party media embeds like YouTube, and underlying tracking scripts).

While these notices appear threatening, analyzing their mechanics reveals an automated, predatory harvesting model designed to trigger immediate financial settlements. We are sharing an operational response guide to expose how these campaigns work and demonstrate how to actively neutralize the risk.

1. Deconstructing the Scam: How Automated Trolls Target Web Infrastructure

These demand letters rely on automated harvesting tools rather than human legal review:

  • Generating Automated Legal Notices: Upon flagging a domain, automated scripts are instantly filling form templates with page URLs and legal boilerplates to simulate individual manual audits.
  • Leveraging Fear of Statutory Fines: The notices are intentionally threatening immediate legal action, calculating that business owners will choose a quick settlement over consulting legal counsel or auditing their technical stack.
  • Ignoring Active Compliance Engines: Scanners are frequently ignoring active client-side script blockers, local caching layers, or privacy frameworks, claiming a compliance violation where none exists or where minimal risk is present.

2. Active Technical Mitigation: How To Eliminate Risks and Remove Vulnerable Plugins

To neutralize any exposure and achieve strict compliance across your web properties, businesses must execute a systematic overhaul of your privacy architecture and consent management engines. This is a time intensive process that looks complicated, but with the right tools at your fingertips, it’s entirely manageable, even by relative novice do it yourself small business and is absolutely worth your attention to shield you from this real risk.

Running this article through your own LLM of choice will serve as a step-by-step blueprint. Mind you, this is not legal advice, this is not 100% fool proof, this is a guide that is designed to point you in the right direction, and if you truly truly want to 100% mitigate your risk, contact your legal council.

Here is exact timeline of actions that must be taken:

Step 1: Deleting High-Risk and Redundant Plugins

  • Auditing Administrative Tools: Actively reviewing all installed WordPress plugins and deactivating unneeded administrative utilities—specifically tools like File Manager Advanced—that are frequently flagged during automated security scans and serve as primary triggers for automated legal letters.
  • Uninstalling Inactive Assets: Completely removing unneeded plugins from the server rather than leaving them deactivated, ensuring their underlying code assets and scripts cannot be indexed or exploited by crawlers.

Step 2: Eliminating Raw Embeds and Sanitizing Links

  • Isolating Unconsented Script Triggers: Locating all legacy media embeds across primary landing pages (/about-us, homepages) to stop unconsented tracking calls prior to user authorization.
  • Converting to Privacy-Enhanced Endpoints: Re-writing raw YouTube embed URLs across the database to use privacy-enhanced endpoints (youtube-nocookie.com), explicitly blocking DoubleClick tracking telemetry prior to user interaction.

Step 3: Deploying Dynamic Script Blocking via Complianz

  • Cataloging Active Cookies: Running site-wide scans to index active cookies, fonts, and scripts across WooCommerce, form plugins, and page builders.
  • Enforcing Dynamic Script Interception: Utilizing a dedicated consent management engine like Complianz to dynamically wrap third-party elements—including Google Analytics, YouTube, Google Fonts, and reCAPTCHA—blocking execution until explicit visitor consent is recorded.
  • Synchronizing Policy Databases: Syncing all detected scripts with open databases (like Cookiedatabase.org) to automatically populate verified cookie descriptions on public policy documents.
  • Publishing Compliance Documentation: Generating required regulatory pages, including standard Opt-out preferences documents, and integrating them directly into footer navigation menus.
  • Activating Global Consent Banners: Enabling live user consent banners across all web properties, ensuring strict compliance enforcement on every incoming visit.

3. Coverage Analysis: How Dynamic Blocking Handles Deep Subpages

A critical question when managing site-wide privacy is whether every single subpage requires manual inspection:

  • Dynamic Theme-Level Interception: Operating the script-blocking engine at the theme/header level ensures that even on deep subpages that haven’t been manually audited, the system is dynamically intercepting and holding scripts before they can execute in the browser.
  • Managing Scanner Index Limits: While free scanning tools typically index up to 50 pages for initial cookie inventory generation, the underlying script blocker is continuously protecting 100% of incoming traffic across all subpages.
  • Ensuring Total Fallback Protection: Combining dynamic script blocking with site-wide database sanitization ensures complete coverage across deep subpages and custom post types.

4. Ongoing Action Plan: Maintaining a 100% Risk-Free Environment

To maintain a hardened, risk-free posture against automated legal bots moving forward, organizations should commit to the following ongoing protocol:

Technical Verification Actions

  • Purging Server and Plugin Caches: Regularly clearing host-level caching (such as WP Engine) and plugin caches (like WP Rocket or W3 Total Cache) to ensure legacy pre-rendered pages are never served to visitors or crawlers.
  • Executing Incognito Verification: Periodically testing inner subpages in Incognito mode to confirm media players remain locked behind consent placeholders until explicit user approval.

Database and Asset Hardening

  • Executing Database Search-and-Replace: Running database search-and-replace routines using utilities like Better Search Replace:
  • This guarantees that even if a client-side script blocker fails, the underlying iframe natively defaults to privacy mode.

Content Publishing & Plugin Hygiene

  • Enforcing Privacy-Enhanced Media Standards: Establishing strict publishing guidelines requiring all newly embedded video or audio assets to utilize youtube-nocookie.com or privacy-enhanced embed codes.
  • Conducting Monthly Plugin Audits: Reviewing installed plugins monthly to deactivate and delete non-essential administrative utilities before they can create new attack vectors.
  • Updating Cookie Inventories: Re-running compliance scans following any plugin or analytics modification to maintain accurate, audit-ready compliance logs.

Seeking the Right Technical Experts: What Your Defense Team Needs

Should you receive a demand letter, when escalating a privacy dispute or preparing a forensic defense, standard web design knowledge is insufficient—you must engage specialized software engineers who can analyze both sides of the application stack. Properly auditing your exposure requires a front-end software engineer to evaluate client-side code, cookies, and browser-level tracking behaviors, alongside a back-end software engineer to analyze the server-side code and data handling logic where the website is hosted.

Because many server environment nuances dictate liability, a crucial preliminary step is establishing hosting architecture: if the site operates on a third-party managed host, server-side data processing may fall under the hosting provider’s infrastructure rather than the site itself. Conversely, if back-end analysis proves the server does not store, transmit, or process the intercepted data, the flagged cookie is functionally a “dead end”—created on the front end, but utilizing no back-end data stream.

While a qualified full-stack engineer can occasionally handle both domains and serve as an expert witness, organizations should carefully vet qualifications and engage separate front-end and back-end forensic specialists if there is any doubt regarding full-stack expertise.

Conclusion: Taking Control of Your Digital Posture

Navigating the modern web means recognizing that automated legal harvesting tools are here to stay. These predatory bots will continue crawling millions of domains daily, fishing for unconsented scripts, legacy embeds, and administrative oversights. While receiving a high-demand notice is unsettling, these letters should never be ignored. Ignoring them can turn a minor technical oversight into an escalated dispute, whereas taking immediate, documented action effectively neutralizes their leverage. By executing a systematic technical cleanup—deleting high-risk plugins, converting legacy embeds to privacy-enhanced endpoints, and deploying site-wide script blocking—you transform your web properties from low-hanging targets into hardened, compliant assets.

Disclaimer: The information provided in this article is for educational and technical risk-mitigation purposes only and does not constitute formal legal advice. Privacy regulations and enforcement standards vary by jurisdiction. If your organization receives a formal legal notice or demand letter, you should consult with a qualified legal professional to evaluate your specific circumstances.

Robert Siciliano, CSP, CSI, CITRMS—recently named one of the 50 Best Cybersecurity Keynote Speakers—is a #1 Amazon best-selling author, CEO of Safr.Me, Head Trainer at ProtectNowLLC.com, and the Architect of The Strategic Human Firewall™. Grounded in his 30+ years of real-world expertise, this content was developed using advanced predictive research tools, with every framework, strategy, and security protocol authored and verified directly by Robert.
Why Do I Need Dark Web Monitoring?

Dark Web monitoring fills an important security gap for individuals and businesses. It has applications in cyber security, reputation management and brand management. By monitoring Dark Web activity, individuals and organizations may be alerted to cyber attacks or data breaches.

Admit it: You search your name on Google to see what’s there. Most businesses pay attention to their online reviews. Some monitor social media to see what customers are saying. Dark Web monitoring completes the picture of your and your organization’s online reputation. It can also tip you off to data breaches or potential cyber attacks.
What Is the Dark Web?

In its broadest definition, the Dark Web is a portion of the Deep Web, which itself is a collection of websites and databases that are not indexed by the major search engines (Google, Microsoft Edge, Yahoo!, DuckDuckGo, etc.). In 2018, CNBC estimated that the Deep Web was 400 to 500 times the size of the Internet that most people use.

The Deep Web itself is benign. It consists of password-protected content, encrypted databases and data, including millions of articles, books, recipes and public records. Some of these can be accessed through specialized search engines, such as a university’s library catalog of digital media or LexisNexis.

Amid those terabytes of data lurks a smaller set of sites that can be accessed with browsers such as TOR, short for The Onion Router, a browser that attempts to conceal the user’s location by routing web traffic randomly across the globe. Promises of anonymity and cover from law enforcement have made the Dark Web a haven for illegal activity. It is where many cyber crimes originate, and where you will find cyber criminals offering their services and software for sale alongside the fruits of their labors: credit cards, login credentials and personal information.

Why Are Businesses Monitoring the Dark Web?

Because a great deal of cyber crime originates on the Dark Web, monitoring is a tool that thwarts and reveals attacks. In some cases, it can be the first warning of a data breach.

Dark Web monitoring begins with a deep dive on selected data points. For businesses, this is most commonly the business name and the names of senior executives and managers. This creates a baseline of information that is known to be compromised, as well as intelligence on any discussions about the business or its leaders among cyber criminals. This information is provided to the business with notes on any areas of concern.

Once the baseline is established, the Dark Web is searched on a regular basis for new information. This may include

  • Mentions of the business or its leaders by cyber criminals, which can signal a pending attack
  • Solicitations to buy or sell information on the business or its leaders
  • Newly posted data, which may include compromised logins for systems, user accounts or personal accounts of the company’s leaders
  • Customer data, such as credit card numbers, exfiltrated from a company’s database

When new information is found, the business receives an immediate alert that can be used to prepare for or stop a cyber attack. In some cases, this is the first evidence of a data breach that compromises customer information.

Dark Web monitoring may also reveal what people are saying about a business and its employees, providing opportunities to repair reputational damage. It can also be used to prevent disgruntled former employees from selling stolen data online after their separation from a company.

How Can I Monitor the Dark Web?

Dark Web monitoring requires specialized software that can access and index the hundreds of thousands of hidden sites that criminals use to communicate. There is currently no free solution, and until recently, monitoring was an expensive service available only to large companies.

Protect Now is pleased to offer affordable small-business Dark Web monitoring that includes a full baseline examination of data about your business and employees, as well as regular updates on any new information that appears online. If someone adds to that information, attempts to buy or sell it or discusses using it, you will be notified immediately so that you can take action.

Online Dating Scams – You May Find Much More than Love Online, and It’s Not Good

These days, if you want to date, there are hundreds of online dating sites and apps out there, but instead of finding love, you may fall for one of online dating scams and lose a lot of money. Most people think that a person has to be “naïve” or “gullible” and the reality is you just need to be human and want to be loved. Sometimes our heart gets in the way of our mind and basic common sense.

What Are Online Dating Scams and How They Work

Online Dating Scams or romance scams are hot topics these days, especially after a report came out from the Federal Trade Commission that said people have lost more than $1 billion in romance scams over the past five years. In 2020, $304 million in losses was reported, and last year, victims of online dating scams lost $547 million.

These reports show that romance scammers are a dangerous breed. They find photos of attractive people or even take on the identity of someone else. Then they create a story and set out to find some victims. They can easily create a perfectly legitimate looking profile, but there is almost always a story about why they can’t meet in person once you get to know each other… they might work on an oil rig, or they are stationed overseas with the military.

Many people who have fallen victim to online dating scams report that they were contacted by these scammers on a dating site, but you really don’t have to be single and looking for them to contact you. They use everything from emails to direct messages on social media to start building a relationship, and many of these start right on Instagram or Facebook.

Romance Scammers Pray on Your Emotions

As master storytellers, cybercriminals involved in online dating scams create a tall tale to con others, and in the process, something always happens — their car breaks down and they need $700 for a repair… their child is sick, and they can’t pay the medical bills… they are a bit short on rent and will be homeless if they don’t pay up… and they come to their “online love” for the cash, but in reality, it’s all a lie. They also might create some sort of reason they need to move funds from one account to another or they have an inheritance that will pay for your lives together, but in order to get it, they need you to be a middleman. In reality, they may be using you to launder money.

You might think that there is no way you would fall for something like this, but millions do each year, and it’s easier to do than you might think. Let’s look at an example.

Finding Your Soulmate

Rebecca D’Antonio was looking for love on the popular dating app, OKCupid. There, she met the man of her dreams, a handsome widowed father from Australia who worked on an oil rig. Rebecca immediately fell for the Aussie, who said his name was Matthew, and they engaged in conversation for weeks before he started needing money for things. Believing him to be her long-distance boyfriend at this point, she was happy to help out when she could. Over time, she ended up sending him around $100,000.

Eventually, Rebecca caught on to the scam, but it was too late. She had to declare bankruptcy, and her life crumbled around her. She ended up confronting “Matthew,” and even explained that she had thought about suicide because she was so distraught about this, and “he” simply responded with “Well, you have to do what you have to do.”

Rebecca wasn’t the only one who fell for “Matthew’s” charms, and eventually, after report after report, it was found that he was actually a member of a Nigerian gang of cybercriminals.

Another well-known case of a romance scam is from the Netflix documentary, “The Tinder Swindler.” The movie is a profile of a man named Shimon Hayut, who went by the alias Simon Leviev. Over time, he was able to swindle people out of more than $10 million in online dating scams.

Look Out for the Lies

The good news is that there are some things that you can look for to determine if a person you meet on an online dating app could be a scammer.

First, most of the time, the person will say that they are not in the US, or they are travelling for an extended period of time. Many will say they work on an oil rig, that they are in the military, or that they are a doctor working overseas with a humanitarian organization.

Next, you should take note of any instances where they ask for money. They often will ask for money for the following reasons:

  • To pay for surgery or medical costs
  • To pay off gambling debts
  • To pay for travel expenses, i.e. a plane ticket
  • To pay for a visa or other travel documents
  • To pay for custom fees

Even if they ask for something that is not on this list, they may ask for a victim to send money in a certain way. For instance, they may want money wired to this, or they may ask for money in the form of gift cards or a reloadable debit card. They do this because they know that there is only a very small chance that they will be caught, and once these transactions are made, it is almost impossible to get your money back.

What to Do if You Think You are Talking to a Romance Scammer

If you think that you are talking to a person who may be a romance scammer, you should start taking steps immediately.

First, never, ever send money to them. If you already have, stop it immediately. Next, you should cut off communication with the person. Reach out to a person you trust, and then pay attention to what your friends and family have to say about this love interest. You should also consider doing some research about what the person told you. Did they say they were in the US Army and stationed overseas? Where? Is this a common scam when you search Google “US Army scammer”? Finally, you want to do a reverse image search of the photos they are sending you. Do they come up as someone else?

Reporting Online Dating Scams

If you believe that you are involved in a scam, you should report it to the FTC. You should also report the person’s profile to the site you met them on.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Apple Releases a New ‘Personal Safety User Guide’ to Help with AirTag Stalking

Over the years, Apple has attracted all types of users thanks to its relatively safe and secure devices and software when compared to other products. However, with the release of AirTags, this has changed a bit, as they can fairly easily be manipulated by people to track others. This has put a lot more focus on Apple products and safety, and it has ultimately led Apple to release a new Personal Safety User Guide, which was created to keep customers safe.

airtagMost of the suggestions and tips that are found in the guide aren’t things that are foreign to people who use Apple products, but there is a new section in the guide all about AirTags. In the guide, Apple explains the numerous features it has applied to AirTags, which were created to stop any unwanted tracking or stalking. It also shares information on what to do if there is an AirTag alert that doesn’t belong to them.
Apple has described this new guide as a resource for anyone who has concerns about harassment, abuse, or stalking through technology. Those who are experiencing this type of harassment or abuse can look at the guide and see step-by-step directions on how to remove access to their information as well as a guide on what they can do to improve their own safety. Though this guide doesn’t technically introduce any new features, it is a good start for people who are looking for a resource to help in these situations.

In this guide, Apple offers a full bulleted list of 13 different tasks that people can use to improve their security. The guide also shares three different checklists, which all provide directions to help people change their settings if they believe that someone might have access to their accounts. Additionally, there are tips on how to stop sharing information with other people.

Meanwhile, AirTags are being used by travelers to locate their lost luggage. Check out our post Be Aware of These Safe Travel Security Tips for more info.

When AirTags were first introduced, the main concern was that people could use the devices to stalk or follow and track other people. As more people have begun to use them, this has turned those concerns into a reality, as there are many reports of people using AirTags to follow others.

To help alleviate some of these issues, Apple introduced a new update that would make the AirTags beep if not near the owner’s phone for a set period of time. There is also a new app that Apple released, called Tracker Detect, which allows Android users to scan for these connections, too.

In addition to stalking, car thieves have also been using AirTags to track down, and eventually steal, expensive vehicles. There is also the fact that parents or partners can use the devices to track their children or significant others, which may bring up some moral issues.

Of course, not all AirTag use is bad. In fact, they can be very useful for things like finding your car in a crowded parking lot, finding your luggage when traveling, or even knowing where your pet is at any time. People also use these tags for much simpler things, like finding their keys in their apartment. Other people report using AirTags for good reasons, too, including tracking where their belongings are during a cross country move.

If you ever have concerns about being tracked with an unwanted AirTag, there are some things you can do to protect yourself. First, any AirTag that is not near its owner will cause an alert to appear on your Apple device. This tells you that an AirTag tracker is close by. They also put out a little alarm if they are away from the owner’s device for too long. Finally, if you are an Android user, you can also download and use the app Track Detect to make sure there are no AirTags nearby.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Protecting Your Accounts from Russian – or Any — Cyberattacks

No matter when you look at the news, there is probably a story about Russian hackers…and if there is not a story about hackers from Russia, there is likely a story about hackers from China or a place like Turkey. There is definitely a chance that any hacker or hacking group could launch an attack against the US, and the government has even briefed companies about what to do if they believe they are at risk.

hacker chest

Just because you are an individual, it doesn’t mean that you are not at risk of a cyberattack, just like a company is. You may be wondering how you can protect yourself, since this is the case. This is a great time to learn more about how to stay safe from cyberattacks – no matter where they come from.

Many cybersecurity threats are coming from what is known as a “Distributed Denial of Service” (DDOS) attack, which is often launched against a website or a financial network. Basically, the hackers push so much traffic to a network or site that it totally crashes, which disrupts business. At this point, the IT team has to focus on getting the network or site back up, which opens a window for a hacker to move in right under their noses.

These attacks can happen at any time, and they can be quite far reaching. Back in 2012, a group of Iranian activists attacked more than a dozen banks in the US, which disrupted all of their sites.

So, what can you do to make sure this doesn’t happen to you? Here are some tips:

In addition to below, check out our post: Russian Hackers: 14 Ways to Protect Yourself and Your Business

  • CASH, YES Cash: Try to keep a little cash available, especially if you are going out of town. This way, you will have money in case a banking network or ATM is not working due to a DDOS.
  • For every banking or financial account you have, make sure you have a strong and unique password. Don’t reuse any passwords, and do not use any social media password for any banking site.
  • Always watch your financial accounts for unusual activity. Check your bank account online or via phone at least once a week, and if you can, every day or two. If there is a problem, it is always best to find it as early as possible.
  • Russian hackers often try phishing scams on social media or via email in order to get access to corporate networks. Never, ever click a link in an email or on social media from someone you do not know. They also use text messages to try to get people to respond with information that will allow them into accounts. Even if it seems like it’s coming from a company you are familiar with or even do business with…confirm everything before you click or give information.
  • Sign up for email or text alerts for all of your financial accounts. This way, if there is a weird transaction, you will be notified immediately.
  • You should also consider signing up for multi-factor authentication for any financial account. When you do, and someone tried to sign into your account…even yourself…the bank or other company will send you a code to the email or phone number they have on file. Even if you put the correct username or password in, you cannot get into the account without that code.
  • Always update all of your apps and software on every device, including phones, tablets, and computers. To make it easy, set these updates to occur automatically, and then you don’t have to worry about it.
  • Don’t believe everything you see online. There are a lot of scams out there, and there is a lot of “news” out there that is not real nor correct. Use common sense before doing anything.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Wi-Fi Hackers Snoop on Your Phone and Laptop: Here’s How They Do It

Wi-Fi is inherently flawed. Wi-Fi was born convenient, not secure. It is likely that you have heard about how dangerous it is to use an unsecured public Wi-Fi connection, and one reason is because a scammer can easily snoop. It is easier than you might think for a person to hack into your device when it is connected to a public Wi-Fi connection. In some cases they may be able to read your emails and messages, access your passwords, or even get personal information like your bank account number.

wiIt’s possible that your router or any router you connect to has been hacked and you won’t know it. A known tactic called DNS (Domain Name Server) hacking or hijacking, skilled hackers, (both black-hat and white-hat) can crack the security of a business or your home Wi‑Fi resulting in a breach. From there, if they are savvy, they’d set up a spoofed website (like a bank, or ecommerce site) and redirect you there.  From here the goal is to collect login credentials or even monitor or spy on your transaction’s on any website.

Think about this too; you are sitting in a local coffee shop working on your laptop while connected to the shops Wi-Fi. Someone sitting near you could easily download a free wireless network analyzer, and with some inexpensive hardware and software (google “Wifi Pineapple”), they can see exactly what you are doing online…unless your device is protected. They can read emails that you are sending and receiving, and they can do the same with texts.

Using a Wi-Fi Hotspot Safely: Tips

 Knowing what can happen when you are connecting to a public Wi-Fi spot, you want to know how to use them securely. Here are some ideas:

  • Don’t automatically connect to Wi-Fi networks. When initially connecting to a wireless network, we are often faced with a checkbox or option to “automatically connect” to the network in the future. Uncheck this and always manually connect. For example, if your home network is “Netgear” and you are somewhere and your device sees another network named “Netgear,” your device may connect to its namesake—which may not necessarily be as safe, potentially leaving your device vulnerable to anyone monitoring that new network.
  • When setting up a wireless router, there are a few different security protocol options. The basics are WiFi Protected Access (WPA and WPA2) is a certification program that was created in response to several serious weaknesses researchers had found in the previous system, Wired Equivalent Privacy (WEP), was introduced in 1997.
  • Confirm the network you are connecting to. Granted, this is easier said than done. There are rogue networks called “evil twins” that criminals set up; they are designed to lure you into connecting by spoofing the name of a legitimate network. For example, you may use what you see as “Starbucks Wi-Fi” to connect while you’re sipping your latte, but you may also see a listing for “FREE Starbucks Wi-Fi.” Or “ATT WIFI” might be real, but a hacker might have “Free ATT WIFI” as a fake network. Which one—if either—is for real? Such setups are designed to lure you in—and once connected, your data might get filtered through a criminal’s device. If you don’t know if a network is safe or not, feel free to ask.
  • This is a bit 101, but when you log into any website, make sure the connection is encrypted. The URL should start with HTTPS, not HTTP. Most sites today encrypt your session automatically.
  • Use a VPN when you connect to a public Wi-Fi connection. A VPN is a technology that creates a secure connection over an unsecured network. It’s important to use because a scammer can potentially “see” your login information on an unsecured network. For instance, when you log in to your bank account, the hacker may be able to record your information, and even take money from your account. VPNs are free to a monthly/annual fee or a lifetime license.
  • If you are using a private network, make sure that you understand that they, too, are vulnerable. Anyone who has some knowledge can use these networks for evil. Always use a secure connection, and seriously, consider a VPN.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Your Photos Are Displaying Your GPS Info!

During the holiday season, people are constantly posting family photos online, especially photos that contain kids. Sure, you think your kids are the most adorable out there, but do you really want the entire world to have access to these pictures? Do you want everyone to know where you live? …and did you know this? When you put photos like this online, pedophiles and predators can get your GPS coordinates.

You might want to put up a photo of your kids and dog opening their gifts on Christmas morning or you and your spouse toasting the New Year, but creeps can easily access the exact location each of these photos were taken, and it’s easier to do than you might think.

How is something like this possible? Each time you take a photo with a digital camera or a smart phone, it creates data called EXIF, of “exchangeable image file format.” This data essentially geotags your photo with the GPS coordinates of where you took the image.

If you remove this data, however, the bad guys can’t see where you are located. However, you have to do this for each and every new photo you want to post online.

How to Remove the EXIF Data

Here are the steps that you should take to remove the EXIF data:

 iPhone:

  1. Locate the picture on your iPhone.
  2. Open it, and tap the Share button.
  3. Tap on Options and in the next pane (up top), toggle off Location and/or All Photos Data.

Android:

From Google Play download the free app Photo Metadata Remover

Windows:

  1. First, right click on the image.
  2. Choose “Properties” to see the data, which should include the time and date that the image was taken.
  3. Click “Details.”
  4. Click “Remove Properties and Personal Information.” This is where you delete the EXIF data.
  5. You might be confused because you don’t see longitude and latitude here, but rest assured, it’s there. All you have to do to see it is to download an EXIF reader.
  6. You can make a copy of the image, which will remove data, or you can manually delete the data.

Mac

Download and run ImageOptim software for Mac

Remember, you have to delete this before you post the photo on the internet. You also might want to consider going back and doing this for all of the photos you have posted.

Obviously, doing this before you post a photo is the easiest way to go about protecting your information, and it will make you much more selective on what you put on social media, as you probably don’t want to have to go through these steps each and every time you post.

Here are some additional tips:

  • Turn off the GPS option on your camera
  • Check out the privacy settings on your social media accounts. Who can see it? Can a stranger?
  • Also, remember, that if you post on one network, like Instagram, the photo might also appear on another network, like Facebook, which has different settings.

This is one of those things that people just don’t even realize is happening. Don’t worry but do something about it now. If you have a lot of photos online, you might be panicking. It’s probably okay, but make sure you change your habits going forward. Also, if you know anyone who posts a lot of personal photos online, make sure they know about this, too.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Avoiding Online Dating Romance Scams

Not too long ago, I heard from a friend, and he told me his mom was scammed. I was immediately intrigued. He goes on to tell me that since his dad died last year, his mom had signed up for online dating. My friend told his mom that online dating can be dangerous, but she blew it off. Soon, she met a man. He was a Sergeant in the US military and stationed in Afghanistan. They exchanged a lot of messages, and soon became close. One day, she got a message from him saying that he had found a large sum of money and he needed help getting it back to the US…and in only three months, he scammed her out of $242,000. Then…he disappeared.

Online DatingThis is only one of the thousands of stories out there. Scammers know that people looking for love, especially women, can be more vulnerable than others. Another guy I know of was meeting women on social media. He was charming them after sending them messages via their inbox, and ultimately tricking them into giving up their personal info. With this, the guy was able to open new lines of credit in the names of his victims.
Preventing Romance Scams

 Here are some tips to stay safe if you are going to date online:

  • Be suspicious of anyone who tries to impress you with romantic or statements that seem cliché.
  • Once they start talking love and marriage and achy breaky hearts and wanting to be with you and I love you this and I love you that, chances are it’s a scammer.
  • Remember, women can be scammers, too.
  • Be wary if the guy you met online keeps showering you with too many complements. He’s trying to be charming but might not have the best of intentions.
  • If you meet someone on a dating site, and they immediately want to exchange numbers after the first message, be cautious.
  • If someone you are newly dating asks for money, run.
  • If they want to come visit you, but then ask you to pay, it’s probably a scam.
  • Don’t talk about how much money you make or have. If he or she keeps asking, tell them you are on a very tight budget.

Who are these scammers?

Well, they might be part of scamming rings, or they might be working on their own. They are probably from a foreign country, and they almost always portray that they have some type of prestigious or exotic job, and in some way, this job is often connected to the scam. If the person says that they have a normal job, don’t get too comfortable. They still could be a scammer. They then will make up an illness or an injury and tell you that they need money.

Protecting Yourself

 Now that you have read this, you should know how to protect yourself from these types of scams. If you don’t, read this article again. Finally, here is one more trick. Right click on the person’s photo, and then click “Search Google for this Image.” If you see the image on another person’s Facebook profile, or if it’s a stock image, you should run for the hills.

None of this is difficult to understand, and it’s all common sense. But, as stated before, common sense can go right out the window when romance is concerned. So, try to have some smarts as you begin a relationship with anyone. Ask questions, don’t take anything at face value, and most of all, share this post to help other people become aware of these scams.

Written by Robert Siciliano, CEO of Credit Parent, Head of Training & Security Awareness Expert at Protect Now, #1 Best Selling Amazon author, Media Personality & Architect of CSI Protection Certification.

Cryptocurrency Fraud and Malware Scamming Investors

Cryptocurrency is hot right now, and whenever something is hot, hackers pay attention. Research has recently showing that more than 10 percent of all the funds that were raised through the ICOs, initial coin offerings, simply disappeared.

CryptocurrencyIt is popular for ICO’s to be used as an early-stage investment form. So, instead of buying shares, investors buy digital tokens. However, the companies that sell these ICOs don’t have any product to give investors except a whitepaper. This whitepaper tells them how things could theoretically work, the investment scheme, but it seems, it doesn’t always happen that way.
Sometimes the Money Just Disappears

Ernest & Young took a look at over 370 ICOs. The firm found that out of the $3.7 billion raised through these offerings, about $400 million vanished. Where did it go? Research shows it went to hackers using phishing attacks.

It’s not clear if the researchers looked at companies that didn’t deliver or disappeared. For instance, one company, Tezos, pulled in about $232 million during an ICO. However, investors got nothing. That looks like fraud.

How Malware is Responsible for Missing Money

At this point, you might be wondering how these scams are happening. One way is criminal hackers using malware. Specifically, it’s Satori. Satori, which is the actual malware responsible for this, is definitely wreaking havoc with investors who are looking for a huge return. Netlab 360, a Chinese-based company, released a report recently pointing the finger at Satori, which is affecting the Claymore Miner software.

By using mining software, investors are able to obtain the cryptocurrency. However, the malware is making this impossible getting in the middle of the transaction. After the malware gets control of the software, it replaces the address of the wallet with one that is controlled by the hacker.

So, the user believes that this currency is coming into their wallet, but in reality, they are doing the work and someone else, the hacker, is getting the currency. What’s even worse is that the owners of the wallets don’t even realize this is happening unless they look at their software configuration.

In total, researchers have determined just over one Etherium coin has been hacked, so it’s not extremely profitable at this point, yet. However, there is great potential, and when it comes to cybercriminals, they will certainly find a way.

ROBERT SICILIANO CSP, is a #1 Best Selling Amazon author, CEO of CreditParent.com, the architect of the CSI Protection certification; a Cyber Social and Identity and Personal Protection security awareness training program.